
HIPAA Control Mappings
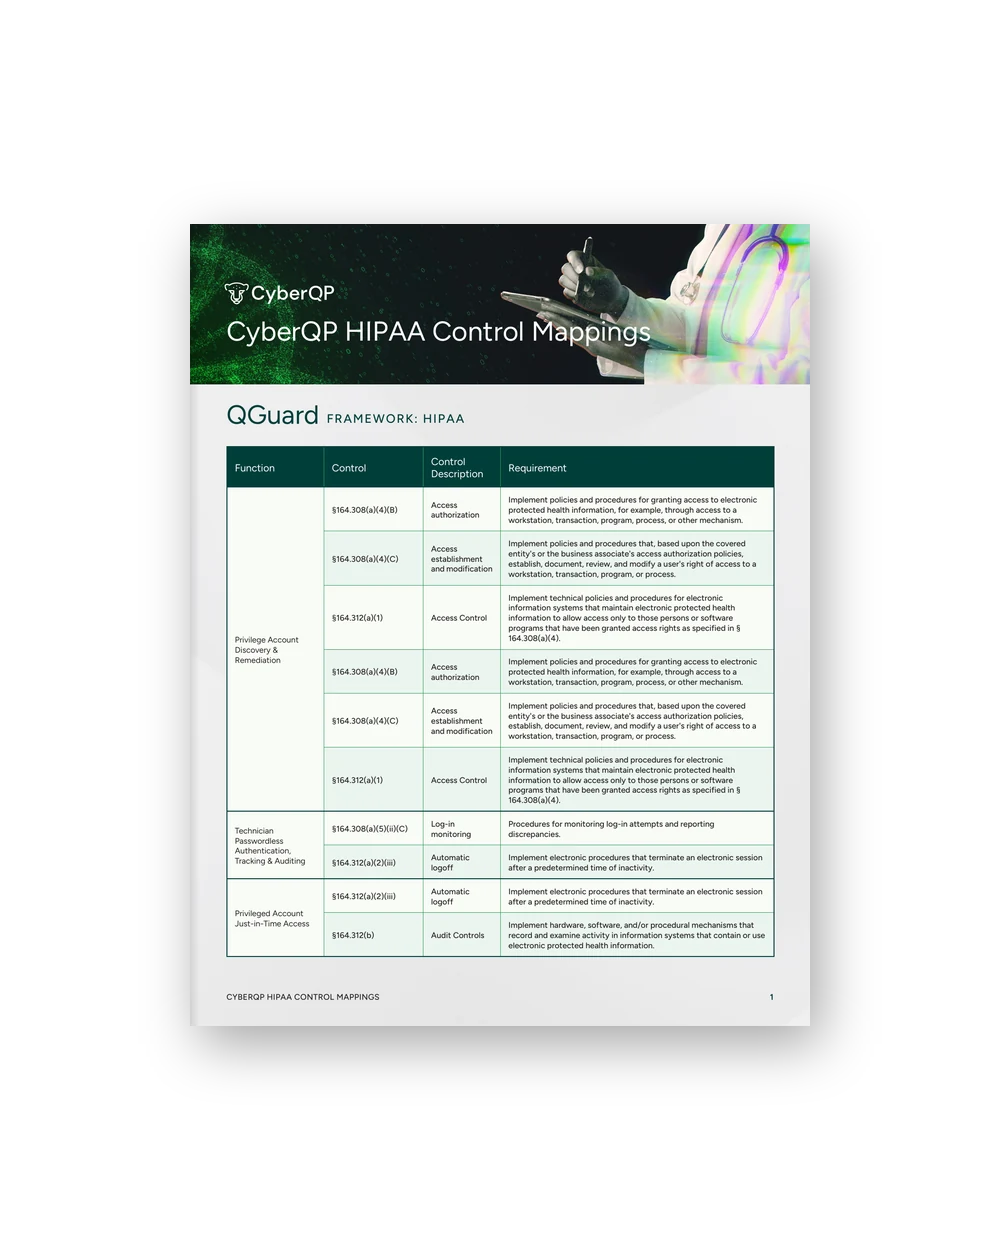
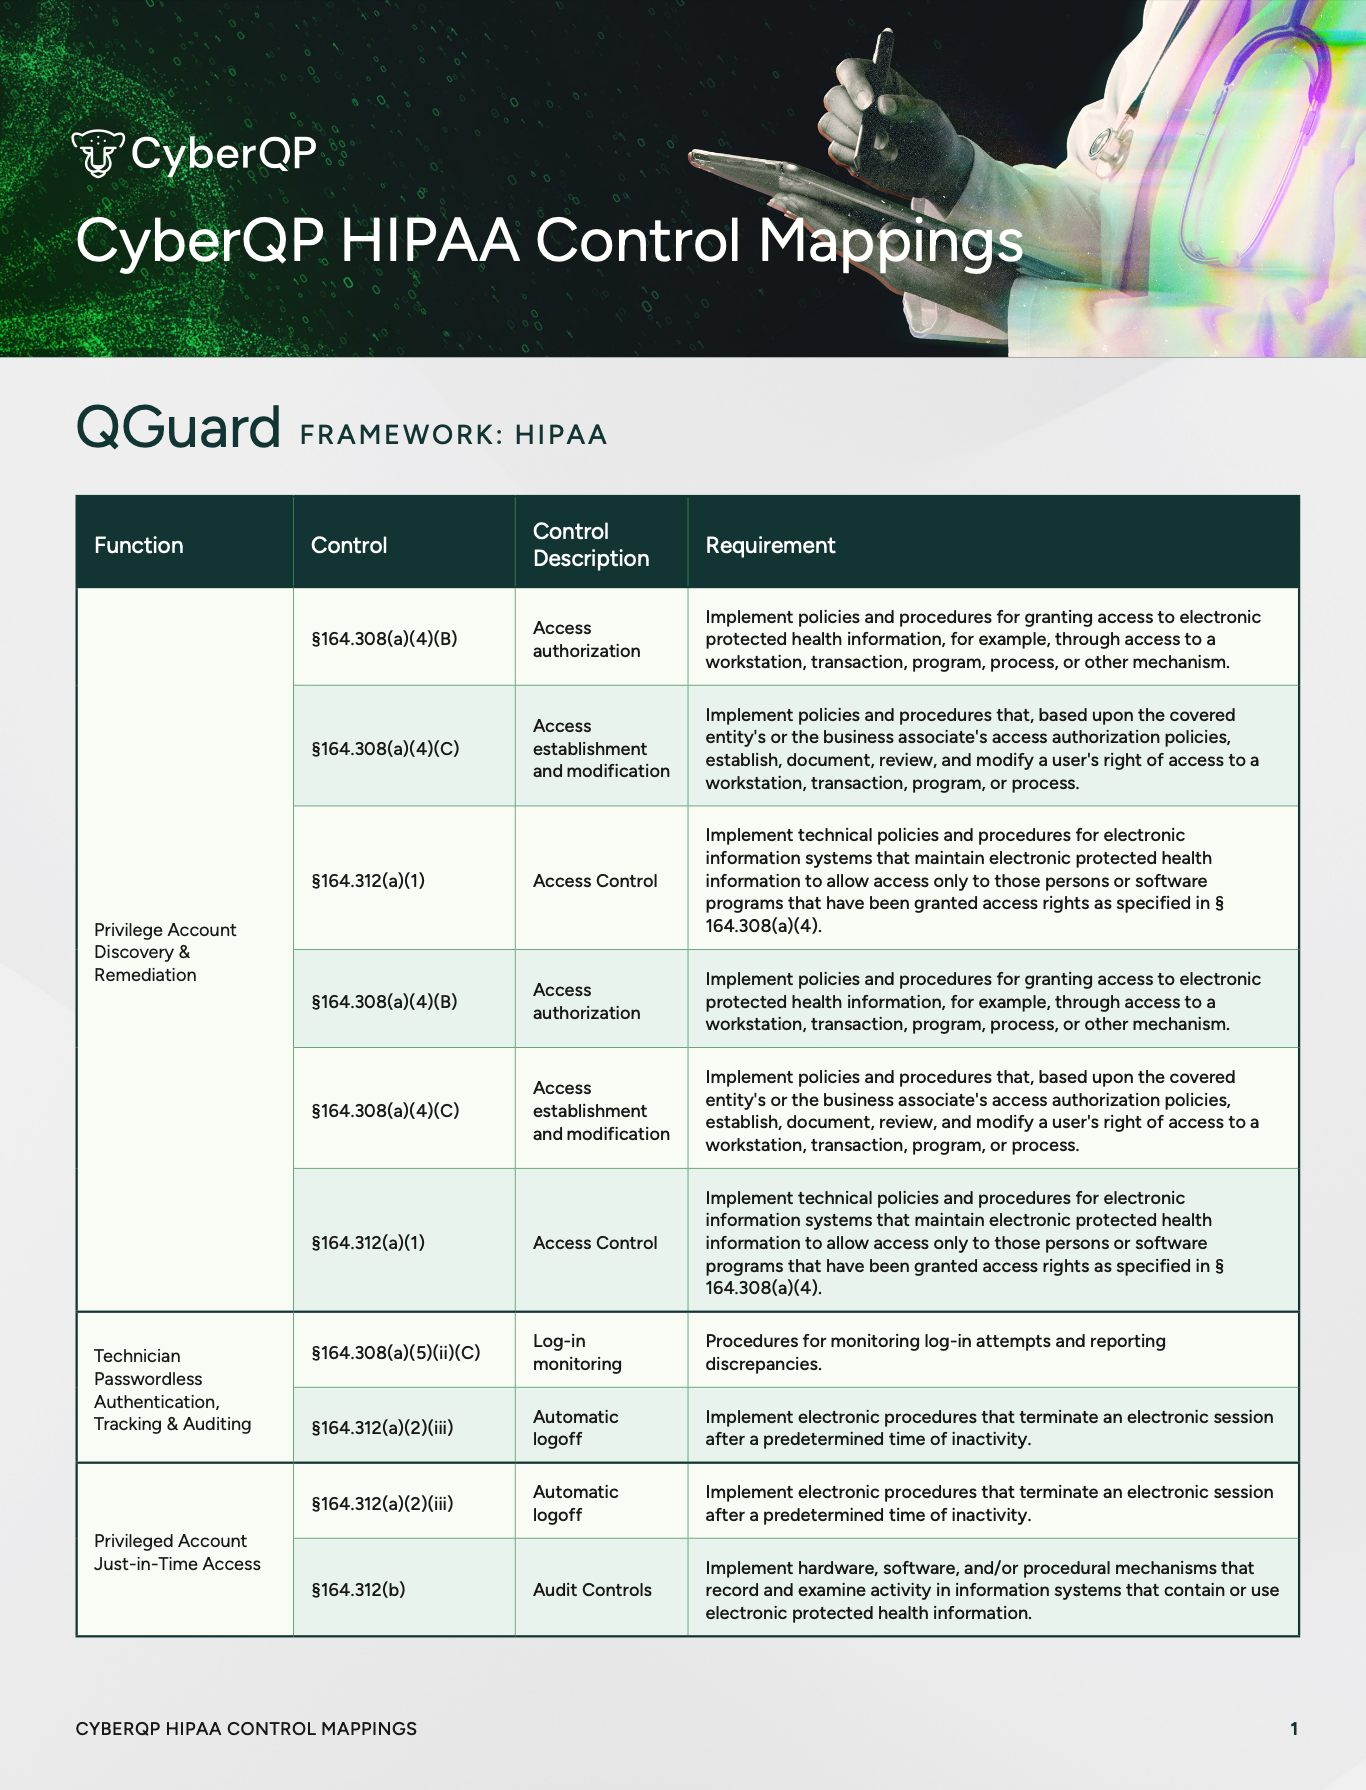
The CyberQP eBook titled "HIPAA Control Mappings" details how CyberQP's privileged access, identity verification, and endpoint security controls align with HIPAA Security Rule requirements, emphasizing identity-first access management to enforce least privilege, verify users at access points, maintain audit-ready compliance, and provide auditors with clear evidence of governance over electronic protected health information (ePHI).
HIPAA Control Mappings | CyberQP eBook
How CyberQP's privileged access, identity verification, and endpoint controls map to HIPAA requirements, and what auditors expect to see as evidence.


EBOOK
HIPAA CONTROL MAPPINGS
Download the HIPAA Control Mapping and Prove Your Access Controls
Where Access Is Granted, Security Must Be Enforced.
Healthcare breaches don’t start with networks, they start with identity. In hospitals and healthcare environments, every login, password reset, and privilege elevation can put ePHI at risk. This eBook explores how identity-first access controls help IT teams enforce least privilege, verify users at the point of access, and maintain audit-ready compliance with HIPAA requirements.
How Privileged Access and Identity Controls Map to HIPAA Requirements
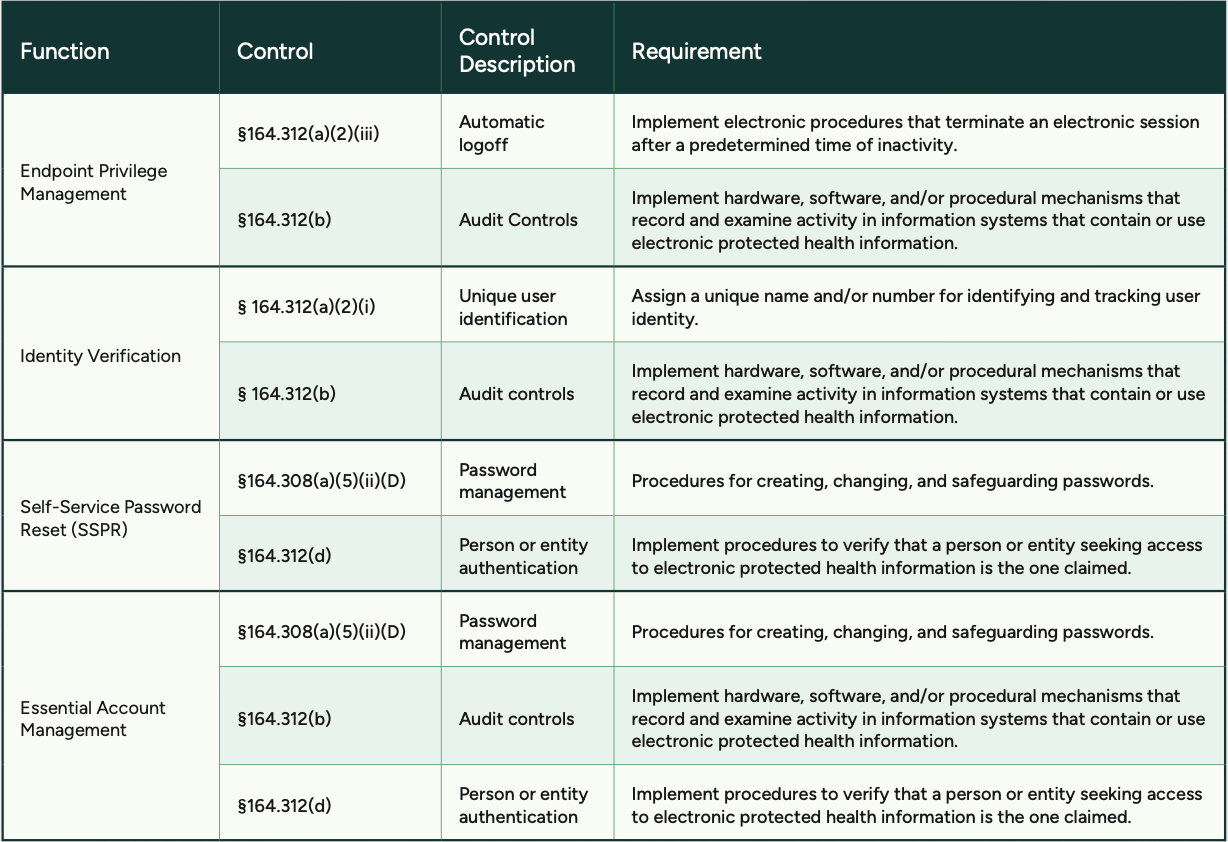
HIPAA compliance isn’t just about implementing security controls, it’s about clearly demonstrating how access to ePHI is governed, verified, and audited. This resource maps HIPAA Security Rule requirements directly to CyberQP capabilities and shows exactly how controls are enforced across healthcare environments.
Instead of relying on assumptions or fragmented documentation, you gain clear, audit-ready visibility into which HIPAA controls CyberQP supports. The result is faster audits and greater confidence when protecting patient data.
How CyberQP Enforces and Audits Privileged Access
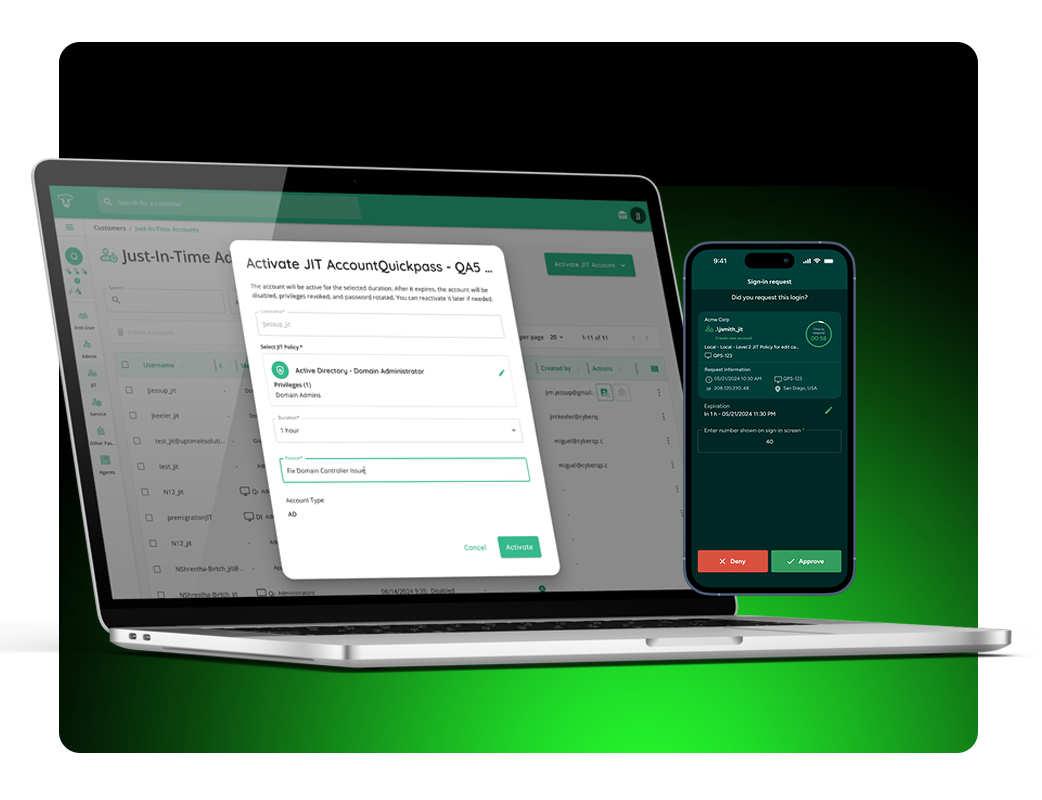
Privileged Account Just-in-Time (JIT) Access
Control area: §164.312(b) Audit Controls
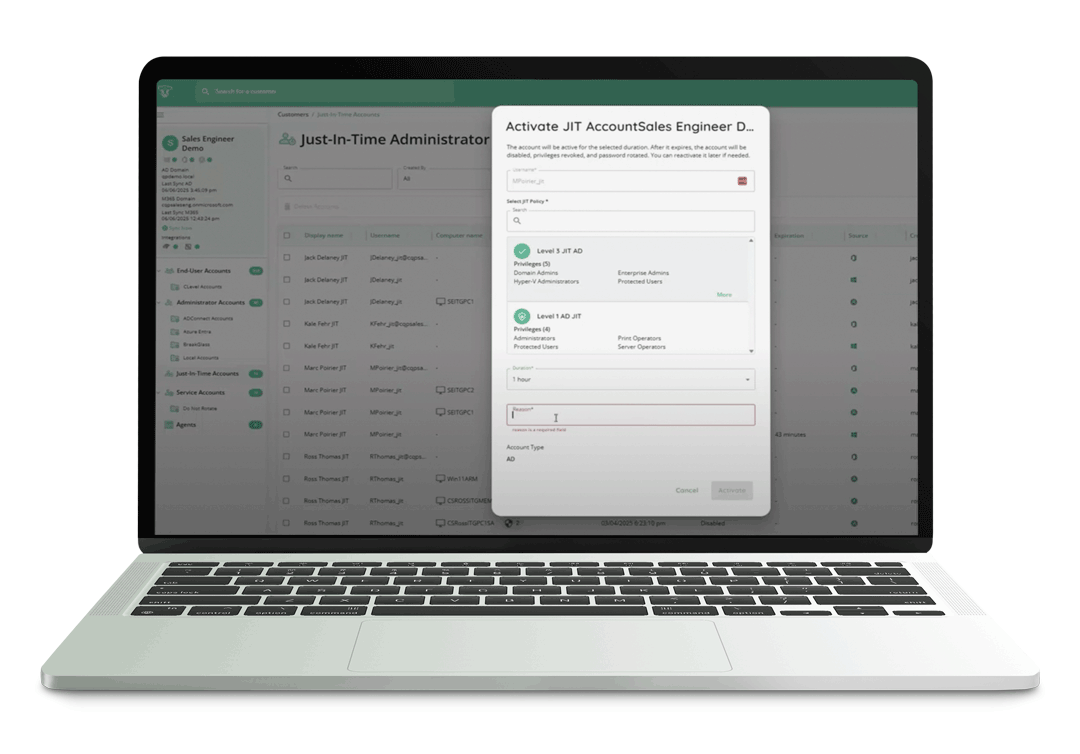
CyberQP’s JIT access enforces temporary, context-based privilege elevation so users and technicians don’t retain standing administrative rights. All JIT sessions are logged and auditable, helping satisfy audit control requirements around monitoring and examining system activity.
Passwordless MFA for Technicians
Control area: §164.308(a)(5)(ii)(C) Log-in Monitoring, §164.312(a)(2)(iii) Automatic Logoff
CyberQP enables passwordless authentication and session tracking for technicians and privileged users. This improves log-in monitoring and auditing, while automatic session termination and authentication events align with controls around termination of inactive sessions.
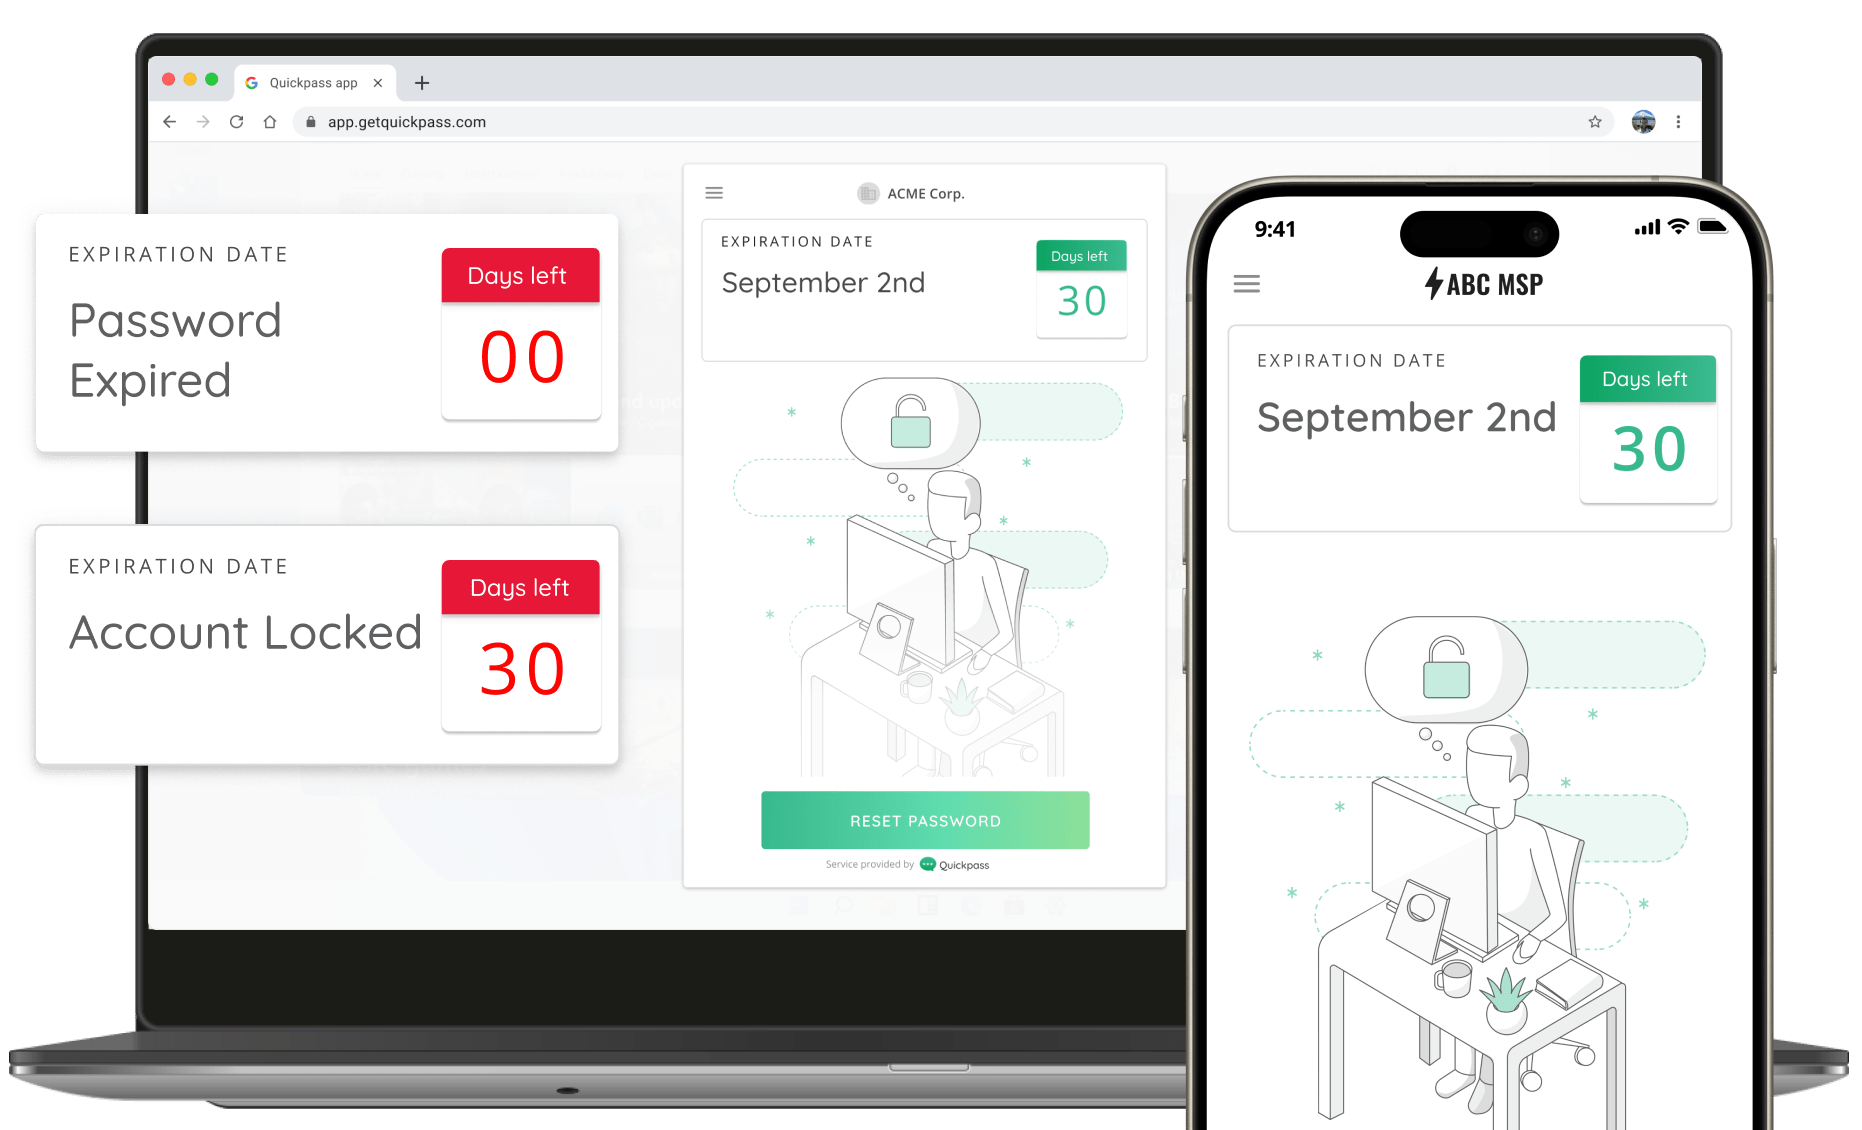
Self-Service Password Reset (SSPR)
Control area: §164.308(a)(5)(ii)(D) Password Management
CyberQP’s self-service password reset workflows are tied to identity assurance, reducing helpdesk risk, and enabling compliant password lifecycle processes.
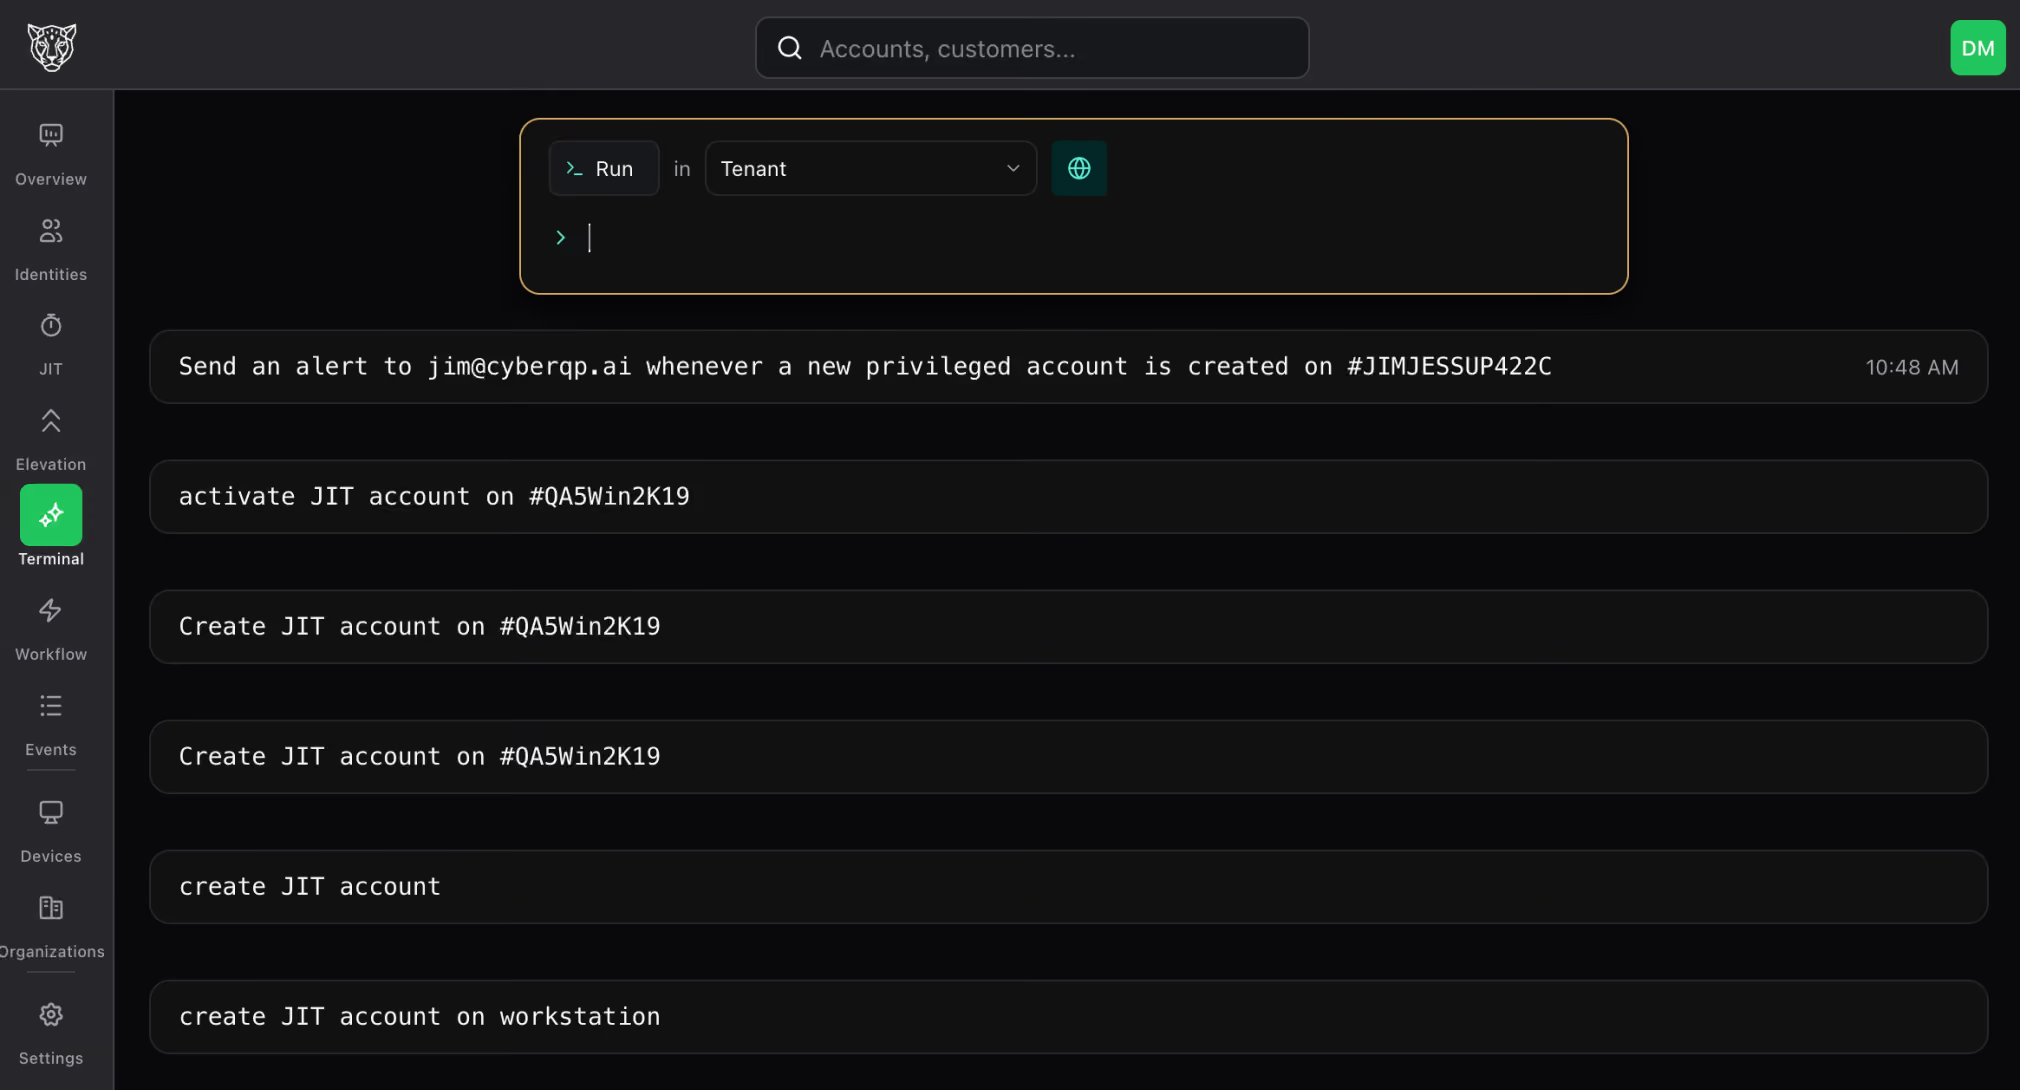
Run Panthera on your own environment

30 days free trial
No credit card required
Products
Pricing QGuard QDesk Integrations Product Tours Product Roadmap Release Notes
Products
Submit a Ticket Partner Portal Trust Center Knowledge Base
Company
Company Leadership Contact Careers
Resources
Resource Hub Blog White Papers eBooks Webinars Success Stories


© 2026 CyberQP Inc. All rights reserved.
Privacy Policy Terms & Conditions Cookie Policy Consent Preferences