
CMMC Responsibility Matrix for Audit Preparation
The CMMC Responsibility Matrix for Audit Preparation is a detailed shared responsibility guide that maps each NIST 800-171 and CMMC 2.0 practice to CyberQP’s enforcement roles and customer obligations, enabling organizations to clearly demonstrate control ownership, streamline audit preparation, and eliminate uncertainty during CMMC assessments.
CMMC Responsibility Matrix for Audit Preparation
A CMMC shared responsibility matrix for privileged access: each NIST 800-171 and CMMC 2.0 practice mapped to what CyberQP enforces and what the customer owns.


Get Audit Ready
Preparing for a CMMC assessment can be complex when control ownership isn’t clear. Our CMMC Shared Responsibility Matrix helps you quickly align CyberQP’s platform capabilities with customer responsibilities so you can streamline audit prep, eliminate guesswork, and confidently demonstrate control ownership.
Stop Guessing, Start Demonstrating Control.
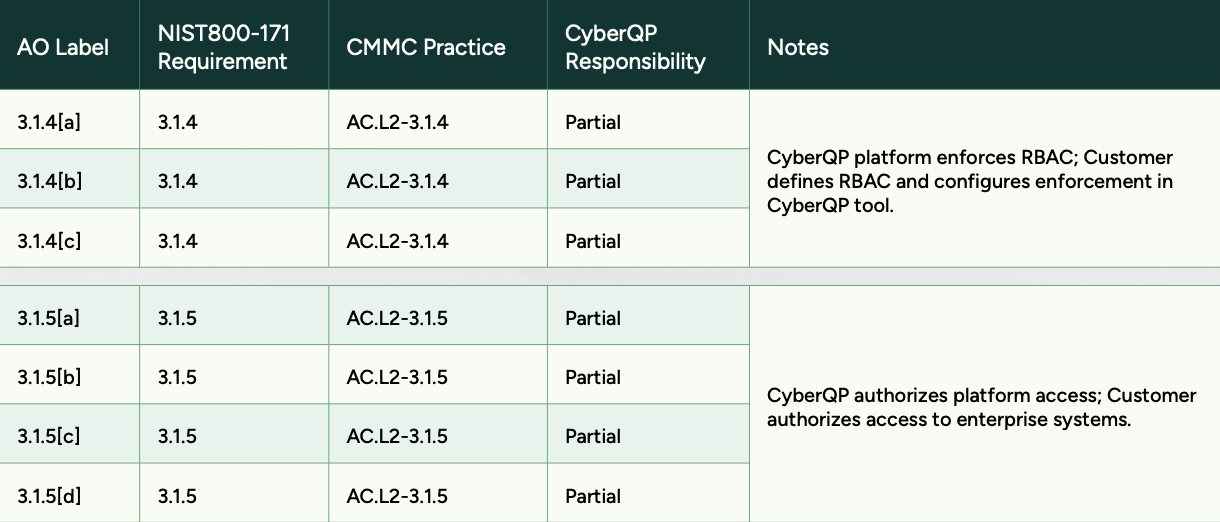
Preparing for an audit isn’t just about having controls in place, it’s about clearly showing who is responsible for what. Our Shared Responsibility Matrix breaks down NIST 800-171 and CMMC practices line by line, mapping each requirement to CyberQP’s role and the customer’s role.
Instead of vague assumptions, you get documented clarity auditors expect: which controls are partially enforced by CyberQP, where customer configuration is required, and how responsibilities align across access control, authorization, and enforcement. This makes audit conversations faster, cleaner, and far easier to defend.
Examples of CMMC 2.0 Security Controls That PAM Supports
Access Control (AC):
Privileged Access Management solutions will help you limit access to sensitive information, keeping the number of security risks as low as possible and minimizing your attack surfaces.
Identification and Authentication (IA):
This requirement calls for security measures to safeguard CUI and only grant access to authorize users, which specifically calls for identity verification before granting access to an organization’s digital environments or devices.
Are You Audit Ready?
This guide gives you clear, documented evidence of how privileged access controls are shared, enforced, and validated against CMMC and NIST 800-171 requirements. If you are preparing for an assessment or tightening controls ahead of one, this reference helps you walk into the audit with clarity and confidence.
Run Panthera on your own environment

30 days free trial
No credit card required
Products
Pricing QGuard QDesk Integrations Product Tours Product Roadmap Release Notes
Products
Submit a Ticket Partner Portal Trust Center Knowledge Base
Company
Company Leadership Contact Careers
Resources
Resource Hub Blog White Papers eBooks Webinars Success Stories


© 2026 CyberQP Inc. All rights reserved.
Privacy Policy Terms & Conditions Cookie Policy Consent Preferences